
Service
Website Security Test and Vulnerability Scan
Find the weaknesses attackers look for before they do. We test your website or web app, review every finding, and send you a clear report with the steps to fix each one.
0K+
New Security Vulnerabilities Published in 2025
0%
of Data Breaches Start With an Exploited Vulnerability
0 days
Average Time to Identify and Contain a Data Breach
$0M+
Global Average Cost of a Data Breach
Powerful Features for Your Business
What the test looks for, and what you get back.
Injection and XSS
We look for the flaws that let attackers run commands or scripts through your forms and pages.
Logged-in testing
With a test account, we check the parts of your app that only customers or admins can reach.
Misconfiguration and headers
Exposed files, weak server settings, missing security headers and certificate problems.
Outdated components
We flag old CMS versions, plugins and libraries with known weaknesses.
Plain-language report
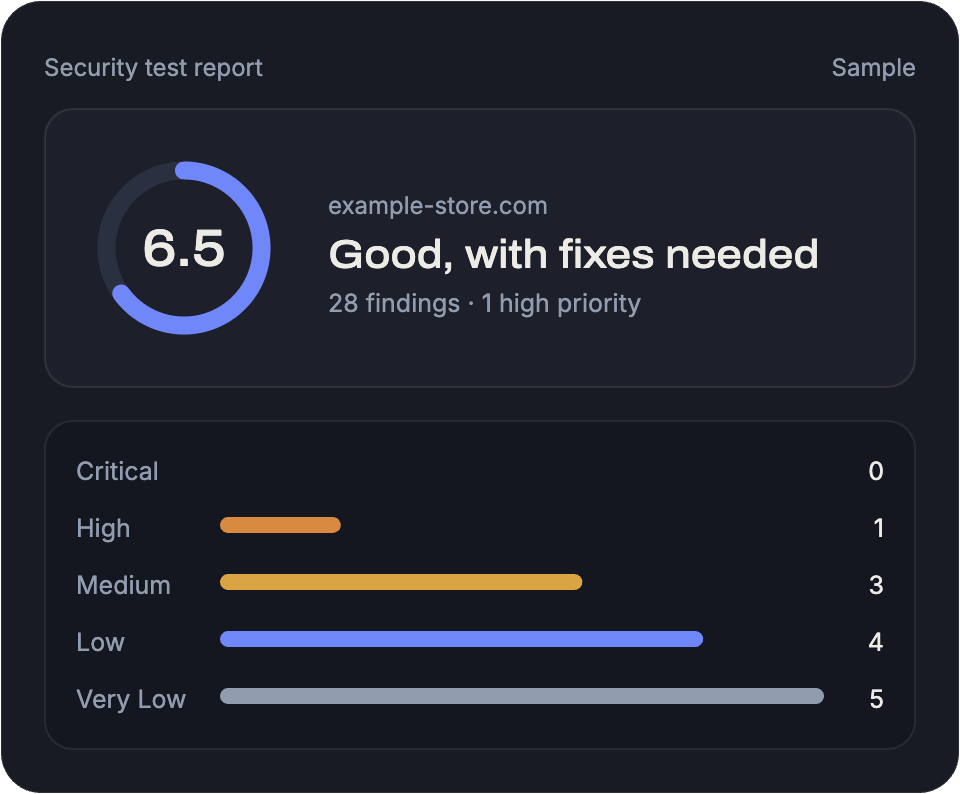
Every finding explained clearly: what it is, why it matters, and how to fix it.
Retest to confirm fixes
On the Complete plan, we test again after you finish fixing and send a second report showing what was closed.
Before and After
This is what a test looks like on one of our own websites: the score and findings before fixes, and after most issues were closed and tested again.
Before7 findings: 2 medium and 5 very low, each listed with how to fix it.
Needs attention
brandify.zone · first test, 19 May 2026Critical0
High0
Medium2
Low0
Very Low5
After retest6 of the 7 original findings fixed and confirmed by a second test.
Good
brandify.zone · after fixes, 4 Nov 2026Critical0
High0
Medium0
Low1
Very Low2
Both are complete reports, exactly as a client receives them.
Enhance Business Growth Through Digital Solutions
Every report is reviewed by our team. We run a limited number of tests each month so that each one gets proper attention.
Essential
BD 249
/ one-timeA clear overview of your website’s security: where you stand and what to fix first.
Contact UsWhat’s included:
- 1 website or web app
- Automated security test
- Findings reviewed by our team
- Khetta report with score and severity summary
- List of findings with location and short description
- Delivered within 7 business days
Complete
BD 399
/ one-timeThe full report, plus a retest after you finish fixing and a second report that shows what was closed.
Contact UsWhat’s included:
- Everything in Essential
- Logged-in testing
- Full detail for every finding: impact and evidence
- Step-by-step fix recommendations
- Findings mapped to the OWASP Top 10
- One retest after you tell us your fixes are done
- Second report with a before and after comparison
- First report within 7 business days
How to Get Started
From your first question to a clear plan, in four steps.
1
Choose and authorize
Pick your plan and sign a short authorization for the website to be tested.
2
We test
After verifying your domain, we run the test. Most finish within a few days.
3
We review and deliver
Our team reviews every finding and sends you the report.
4
Fix and retest
Your team fixes the issues using the report. On the Complete plan, tell us when you are done and we retest and send a second report.
More About Service
Most businesses find out about a security weakness only after someone has used it. A Khetta security test shows you the weaknesses first, in order of priority, with a clear way to close each one.
We run an automated security test against your website or web app, covering the weaknesses attackers use most, including injection, cross-site scripting, broken access control, misconfiguration and outdated software. Our team then reviews every finding, removes false alarms, and writes the report in plain language, so you know what to fix first and how. On the Complete plan, we retest once you have finished fixing and show you what has been closed.
Frequently Asked Questions
Is this a penetration test?
It is an automated security test reviewed by our team, not a manual test by a certified penetration tester. It finds the common weaknesses attackers use and gives you a clear plan to close them.
Will the test harm or slow down my website?
We agree the timing with you first and recommend running it outside your busiest hours. For critical systems we can test a staging copy instead.
How long does it take?
Most tests finish within a few days. Allow up to 7 business days from verification to a reviewed report.
Do I need to give permission?
Yes. You sign an authorization naming the website, and we verify that you control the domain before any test starts. We only test what you are authorized to test.
What do I need to provide?
The website address, a contact person, and access to add one verification record to your domain. For logged-in testing, a test account.
What is in the report?
An overall score, a summary for decision makers, every finding ranked by priority, plain-language explanations, and the steps to fix each one.
Is my report kept confidential?
Yes. Your report is shared only with the contact you name. We can sign an NDA on request.
Does this make me compliant with PCI DSS or ISO 27001?
No. The report maps findings to the OWASP Top 10, but it is not a compliance certificate.
Can I retest after fixing the issues?
Yes, with the Complete plan. When you tell us your fixes are done, we run a retest and send a second report that shows what was closed. The Essential plan includes one test and one report.
What payment methods are accepted?
We accept bank transfer and BenefitPay.
How do I get started?
Choose a plan from the page and submit a request. We will send the authorization form and arrange the test.